PHISHKIT
Run an authorized
phishing assessment,
end to end.
A local desktop app that wraps evilginx, an AiTM proxy, together with a native email campaign engine into one workflow: target, phishlet, lure, template, recipients, campaign, results, and a captured session. Expert operators keep full control, and a non-technical user can run a safe click-through campaign out of the box.
AUTHORIZED USE ONLYUse phishkit only with explicit written authorization from the owner of the targeted systems and people.
- evilginx AiTMproxy capture
- mail enginedraft · test · launch
- sessionsattributed
- awareness modeclick-only
- wizard + advancedtwo audiences
- CLIheadless
What is phishkit?
phishkit is an open-source platform for authorized adversary-in-the-middle testing and phishing awareness. It builds on evilginx2 and a native campaign engine so one tool runs an engagement from setup to a captured session. It is alpha software, and it is meant only for systems and people you are authorized to assess.
- [*]
AiTM capture evilginx captures what an attacker would actually get, attributed deterministically back to the campaign attempt.
- [*]
Native mail engine A draft, review, test, and launch composer bound to a target, lure, sender, template, and recipient list, sending through your own SMTP or ESP.
- [*]
Tracking and reporting Delivered, opened, clicked, and bounced tracking, with CSV, JSON, and redacted reporting.
- [*]
Sessions view A timeline per captured session with masked credentials, a token and cookie summary, export, and gated replay.
- [*]
Awareness mode A click-only training path that never captures credentials.
- [*]
Two audiences A guided wizard and a preset scenario library with safe defaults, layered over full Advanced controls for expert operators.
- [*]
Auditable by design Sender and content are snapshotted at campaign creation, and sessions trace back to the attempt that produced them.
- [*]
Desktop and CLI A supported Tauri desktop app with a headless phishkit CLI for scripted runs.
Get started
- 1.
Install
- 2.
Start a guided assessment
- 3.
Try the AiTM capture against the local cookie demo
- 4.
Review results
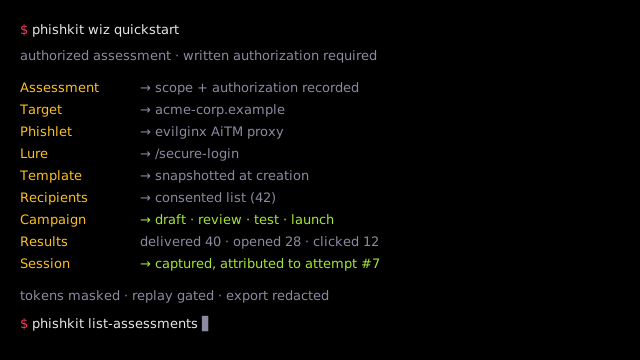
One assessment, end to end
Each stage is bound to the one before it, so a campaign always traces back to a target, a lure, and an authorization.
- 01
Assessment
Open an engagement with its scope and written authorization recorded.
- 02
Target
Set the domain and systems you are authorized to assess.
- 03
Phishlet / proxy
Configure the evilginx AiTM proxy and the phishlet it runs.
- 04
Lure
Pick the named lure path the campaign points recipients to.
- 05
Template
Compose the email. Sender and content are snapshotted at creation for auditability.
- 06
Recipients
Load the consented recipient list for this engagement.
- 07
Campaign
Draft, review, test, then launch, with scheduling and send windows through your SMTP or ESP.
- 08
Results
Track delivered, opened, clicked, and bounced, with CSV, JSON, or redacted reporting.
- 09
Session
Captured sessions are attributed back to the campaign attempt, with masked credentials, a token summary, export, and gated replay.
Live from GitHub
openhat-security/phishkit · GPL-3.0 · 23m ago · ★ 0 · 17 commits
FAQ
What is phishkit?
A local desktop app that wraps evilginx, an AiTM proxy, with a native email campaign engine into one authorized assessment workflow, from target and proxy through to a captured, attributed session.
Who is this for?
Only people with explicit written authorization from the owner of the targeted systems and people. phishkit drives an AiTM proxy, sends email, and handles captured credentials and live session tokens. Read the authorized-use and threat-model docs before running anything.
Can I run a campaign without capturing credentials?
Yes. Awareness mode is a click-only training path that never captures credentials.
How does it send email?
Through your own SMTP server or ESP. The composer binds a target, named lure, sender, template, and recipient list, with scheduling, send windows, and delivered/opened/clicked/bounced tracking. Sender and content are snapshotted at creation.
What happens to captured sessions?
evilginx captures what an attacker would get, attributed deterministically to the campaign attempt. The Sessions view shows a timeline, masked credentials, a token summary, export, and gated replay.
Does it suit non-technical users?
A guided wizard and a preset scenario library with safe defaults cover business users, with full Advanced controls underneath for expert operators.
Is it stable?
No. phishkit is alpha (v0.1.1-alpha.1). Expect breaking changes. There is no OS-vendor-signed installer yet.
Is phishkit open source?
Yes, under GPL-3.0. It orchestrates upstream projects, notably evilginx2; you are responsible for complying with their licenses. Requests to enable unauthorized use are out of scope.
Collaborate
Want to contribute, or looking for red-team and awareness-engineering work?
phishkit is open source under GPL-3.0. It lives at OpenHat Security alongside OnionGate, truffles, and RunHug. If you want to work on phishlets, the mail engine, session attribution, or safe awareness scenarios, open a discussion or email Adam. phishkit is for authorized use; requests to enable unauthorized use are out of scope. Report security issues privately per the security policy.